Talk to us Risks to Watch

Cyber Hygiene for Data Security & Data Privacy

Cyber Hygiene and Cyber Security Spending

Good health is a priceless asset! To stay healthy and fit, more and more people ensure health hygiene. In short, we don’t mind footing increasing healthcare bills as maintaining health hygiene helps to avoid incurring bigger unforeseen health-related expenses. 

Similarly, for modern organizations, cyber hygiene is desirable. 

Organizations adopt adequate IT security measures and policies to ensure a ‘healthy’ IT environment. There are several attributes of cyber hygiene that ensure IT security safeguards of a digital infrastructure. This requires continuous assessment of the security policies and mechanisms. 

Nevertheless, the question is, how many organizations regularly conduct assessment of IT security preparedness to ensure a safe and ‘healthy’ IT environment? 

Even though there is an assessment, are the organizations adopting adequate IT security measures to ensure a secured IT environment? Shockingly, however, 40% of global business organizations spend nothing or are under-invest to secure their information assets from cyber threats.


5 Reasons why today’s Organizations need ARCON | UBA


Cyber Hygiene and IT Risk Mitigation 

Cyber hygiene is nothing but the security practices that maintain IT systems’ health and improve cybersecurity. These routine practices ensure the security of digital identities, safe access control mechanisms, continuous monitoring of end-users and other safety practices like network security. 

Cyber hygiene wards off IT threats like:

  • Data breach
  • Loss of data privacy
  • Malicious end-user activities
  • Anomalous end-user behaviour
  • Cyber espionage
  • Unauthorized access
  • Insider threats
  • Misuse of elevated access rights
  • Non-compliance to the global standards

Cyber hygiene does not necessarily depend on adequate security policies adopted by organizations. It largely depends on the IT culture, employees’ sincerity and willingness to follow the rules, and cyber knowledge/ skills. Even if the policies and processes are in place, there can still be concerns over the relevancy of the policies as per situational demand. It also requires regular audits to assess cyber security preparedness of the organization. Any kind of vulnerability anywhere can pose the biggest threat to the digital assets of the organizations. After all, cyber crime is the greatest threat to every company in the world in the digitalization age.

Cyber Hygiene and Right Solutions

In the modern IT environment, the threat patterns have evolved a lot. In addition to malicious network traffic, threats like cloud-based identity theft, social engineering attacks, cyber espionage, unpatched security vulnerabilities, IoT-based threats and privileged access misuse tops the list of modern cyber threats.

Against this backdrop, cyber hygiene is the foremost priority of every industry today. Adoption of these solutions cannot only ensure safe day-to-day IT operations but also compliance with global regulatory standards. The solutions that top the requirements are:

Unified Identity Governance Platform – A unified identity governing engine such as Identity and Access Control Management (IDAM) solution enables IT staff to control, monitor and audit every digital identity. Centralized control mechanism helps to discover and on-board every digital identity for better management of the lifecycle of identity. Moreover, Privileged Access Management (PAM) solution, a subset of broader IDAM helps to identify security vulnerabilities in privileged access environments with advanced access control mechanisms even at a granular level.

User Behaviour Analytics (UBA)– Internal frauds, data abuse among other identity-related IT incidents happen due to the lack of end-user behaviour monitoring. For that, analyzing end-user behaviour is mandatory. Solution like UBA, with the help of its AI/ML-based algorithms, helps organizations to identify risky behaviour profiles and flag alerts beforehand. It helps organizations to take necessary steps well in advance before any probable IT catastrophe.

Endpoint Privileged Management (EPM)– Misuse of endpoints is on the rise. With a comprehensive mapping of every IT environment, EPM solution ensures a strong user validation mechanism and improves endpoint governance. Moreover, restricted elevations (just-in-time endpoint privilege) control endpoint access in every IT environment and help the organizations to mitigate risks of application abuse. 

Conclusion

Health hygiene is the best way to live a healthy life. We hardly have any choice over this. Similarly, digitalization has necessitated cyber hygiene in every layer of the enterprise IT ecosystem. A renowned American author Katherine Neville once said, “Privacy – like eating and breathing – is one of life’s basic requirements.” Today, data privacy and data security have become so important that they are being associated with the ‘basic needs’ of humans.

Are we doing enough to be compliant with the GDPR?

GDPR Completes its Third Anniversary

On 25th May, 2018, the European Union adopted the General Data Protection Regulation (GDPR), one of the most comprehensive compliance recommendations on data protection.

As the wave of digitization swept across the world, organizations and regulatory authorities felt the dire need to protect personal identifiable information (PII) and confidential business information.

It was felt that data processors and data controllers must centralize their focus more on secured access management in an IT environment. GDPR helped the organizations to mandatorily ensure adequate and relevant IT security policies and mechanisms.

GDPR: What is it?

GDPR compliance is strictly applicable to all EU-based organizations that generate, store and process personal information of EU citizens like names, addresses, email Ids, personal security numbers etc. The GDPR ensures secure processing of the confidential information of EU citizens with their consent.

Even non-EU organizations that process and stores data of EU residents have to comply with the mandates given by GDPR.

In order to implement GDPR successfully, a data controller and data processor play a key role in maintaining adequate information security controls. Moreover, it is highly crucial for third parties like Managed Service Providers (MSP) and Cloud Service Providers to comply with the regulations.


Watch this video to learn how organizations can ensure essential IT security requirements for robust IT security posture.

Read More


Fundamentally speaking, every aspect of our lives revolve around data. Starting from personal records, to social media footprint and from finances to government records and retailers – everywhere we are bound by our digital identities.

At the same time, analyzing from a business perspective, every organization strives to maintain data security, data integrity and data privacy every day. By following the terms of GDPR, organizations could ensure that their confidential data assets are gathered legally and bound by the strict IT security policies.

GDPR Violations and Penalties

Till date, numerous organizations have been fined millions of euros for GDPR violations. An international airliner, a global hospitality chain, the world’s search engine giant, telecommunications giant, a global lifestyle chain… To name a few, have been penalized for violating GDPR.

The cost is huge for failing to comply with the GDPR. Organizations can be fined up to 4% of annual global turnover or €20 million (whichever is higher) in case of non-compliance with the regulation.

To avoid these hefty non-compliance penalties of GDPR, Privileged Access Management (PAM) definitely plays a crucial role. ARCON | PAM offers a unified policy engine to ensure that anyone accessing the database from anywhere in the world is authenticated and authorized. Not only that, rule and role-based granular level access control ensures security at all levels in the network periphery. This is what GDPR seeks from all the organizations.

Are we doing enough to stay GDPR compliant?

This is a million-dollar question. Effective compliance largely depends on the enterprise data security policies and data security preparedness. The mandates of GDPR clearly mention that it expects organizations to reinforce robust IT security frameworks in every layer of the IT ecosystem. Accumulation, storage and transfer of every data needs to be identified, recorded and the risk areas should be detected and mitigated. However, the question is, which security measures are we taking to stay GDPR compliant?

Per our research, the latest (May 2021) below statistics shows a different picture though.

  • GDPR fines have risen by nearly 40% recently.
  • Total penalties under the GDPR totaled $191.5 M.
  • The authorities of GDPR recorded 19% more data breach incidents in the last 1 year

GDPR Compliance and the role of ARCON Privileged Access Management

Deploying ARCON Privileged Access Management is the easy, convenient and transparent way to ensure GDPR compliance. The solution answers the below questions in affirmatives:

  • Does it maintain data privacy and security of all the data logs? Is this data encrypted?
  • Is there any mechanism to notify the authorities about any data breach incident within 72 hours?
  • Do the privileged identities face authorized access only?
  • Is the principle of least privilege applicable?
  • Is there any granular level access control over the end-users?
  • Are there any secured third-party (MSP & IaaS service provider) access to the IT systems?
  • Is there any continuous monitoring of every activity around critical applications?
  • Are there any real-time threat analytics capabilities?
  • Is it capturing logs of every critical session for audit trails and identifying anomalies?
  • Is there any centralized policy engine to authenticate end-users before granting access to critical systems/ applications?

Conclusion

In a nutshell, Privileged Access Management can “Kill two birds with one stone”! In the digital age, every organization has a commitment to strengthen data protection mechanisms. ARCON | PAM is a highly effective solution to ensure ‘secure IT environment’, while it also paves the way for meeting compliance requirements. What could be a better way to stay resilient to modern cyber threats and at the same time compliant to the global regulatory standards like GDPR?

ARCON Shines Brightly at the GEC Security Symposium 2021

ARCON at the GEC Security Symposium

Almost after a year and a quarter, it was great to be back at one of the keenly anticipated events — GEC Security Symposium. 

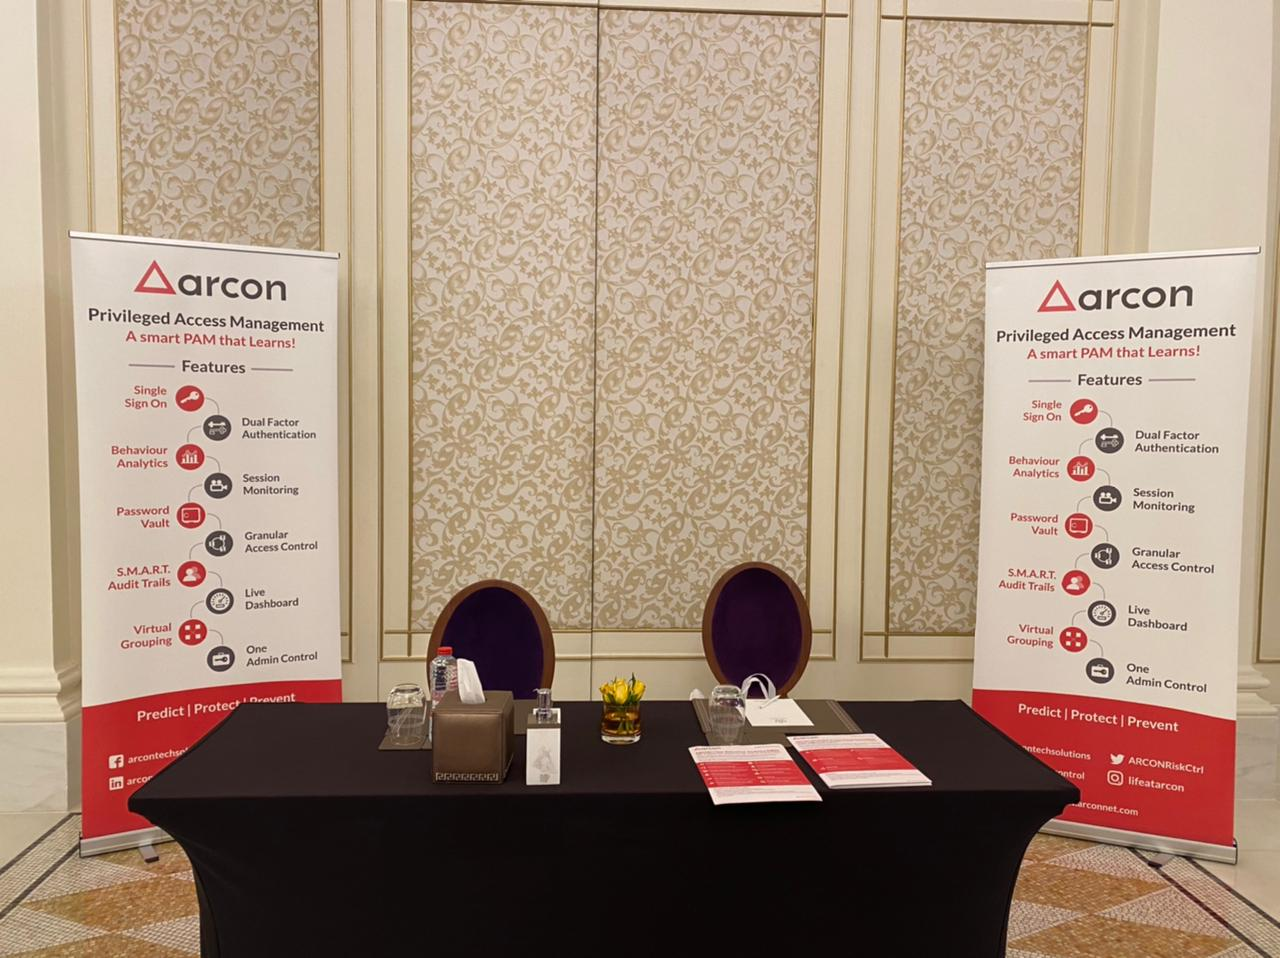
ARCON sponsored and participated at the GEC Security Symposium. The leading IT players and solution providers along with IT heads from the Middle-east region gathered at the event to engage in knowledge sharing sessions, focused especially on the modern-day emerging IT vulnerabilities. This year, ARCON was the privileged access management partner.

Organized at Palazzo Versace, Jaddaf Waterfront, Dubai, the GEC summit is an annual event that takes place in this vibrant city. 

The GEC Security Symposium and CISO Awards 2021, presented by Cyber Sentinels, explored the real context of end-to-end security in today’s IT environment. The organizers recognized the leading players in the industry who are relentlessly into R&D to solve the emerging IT security threats and are developing cutting edge solutions that meet all the enterprise IT security demands. The event offered an excellent platform for collaboration between the IT heads from leading organizations and leading IT security vendors from across the world. 

GEC Security Symposium - image 1

GEC Security Symposium & Cyber Sentinels Future Security Awards

The IT security community believes that the remote work culture and remote workplace would increasingly be a norm as many companies are prioritizing employee health and wellness amid uncertainty arising from the pandemic.

Nevertheless, the remote workplace poses unprecedented security challenges for the organizations. To mitigate the emerging cyber risks, especially secure remote access, organizations are left with no choice but to implement transparent and comprehensive IT security policies and take proactive measures to ensure business data safety and integrity.

In the last fifteen months, it has been observed that organizations worked remotely where the privileged users accessed critical applications/ systems and confidential databases as a part of daily IT operations. 

How can we ensure security of business data in remote work conditions? 

ARCON’s Privileged Access Management (PAM) addresses the challenges with the help of robust security tools. ARCON developed a host of robust security tools such as Application Streaming Server, End-user Behaviour Monitoring (ARCON PAM’s UEBA agent that leverages AI/ML to detect endpoint risks on real-time basis, Just-in-time privileges capability among many that offered secure remote access on ‘need-to-know’ and ‘need-to-do’ basis. 

The solution prevents malicious insiders and other access management associated risks while working remotely. ARCON also bridges the gap between low-friction and high security identity management requirements which raises end-users’ productivity. 

The cyber threat landscape is increasingly getting vulnerable every day. There is no limit to betterment when it comes to upgrading the enterprise security posture. 

Keeping that in mind, the Cyber Sentinels Future Security Awards 2021 recognized the security vendors, VADs, System Integrators and Resellers who have walked the extra mile to meet the security needs with innovations and customizations of their solutions. The value for money as per security offerings have also been taken into consideration.

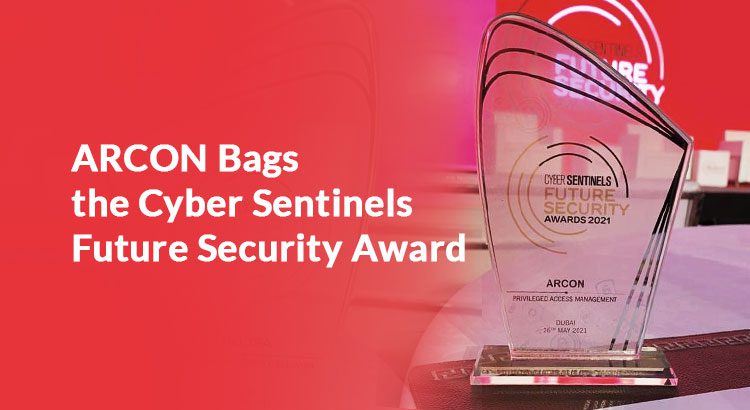
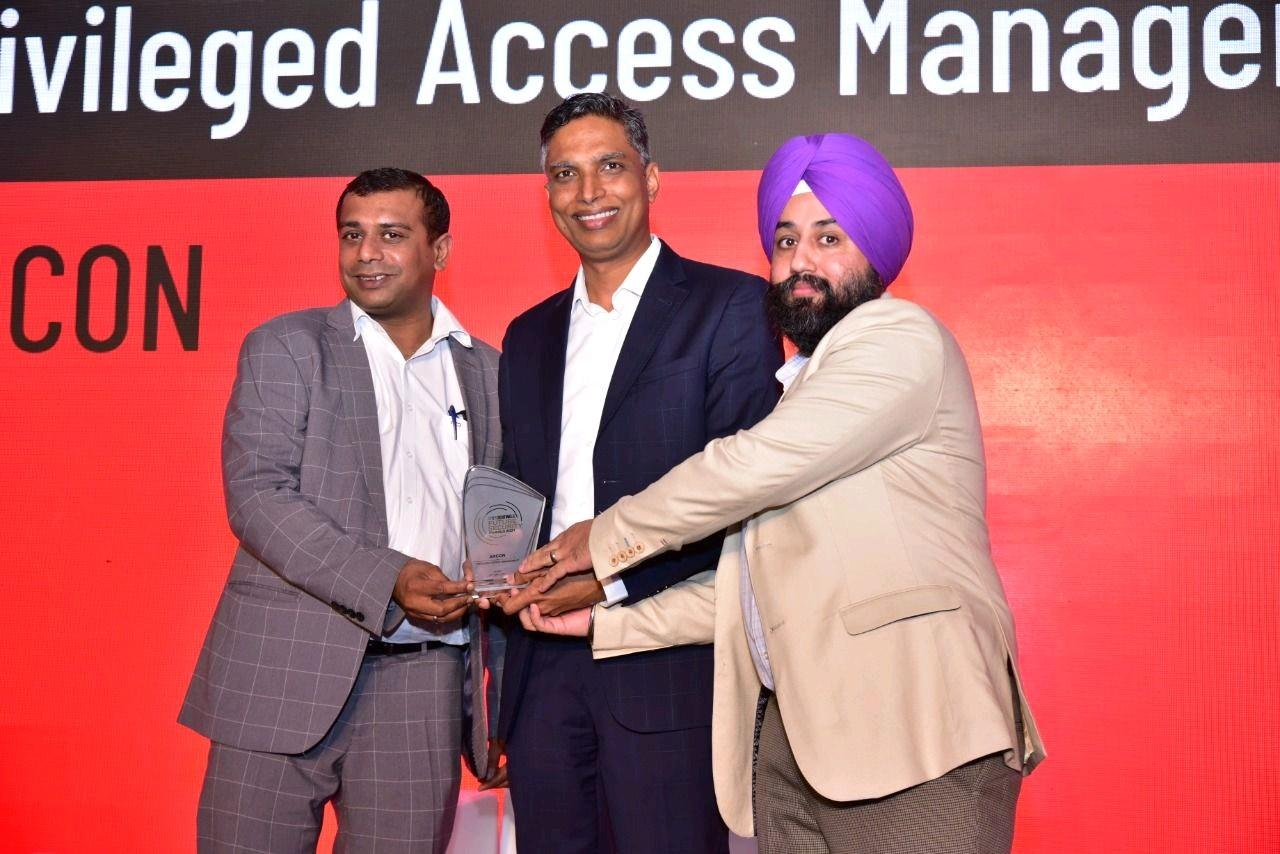
ARCON received the coveted award for Privileged Access Management and received a big round of applause from the audience. The global CIO Forum recognized ARCON’s contribution towards securing global organizations’ information assets with the help of its highly-mature Privileged Access Management (PAM) solution. 

While receiving this award, Mr. Nikhil Sanghvi, Director Sales & BD, and Regional Head, Middle East, ARCON, said, 

We would like to thank GEC Media and Global CIO Forum for recognizing our efforts and rewarding us. This only shows that we are on the right track of our relentless work of serving every global organization with their IT security needs.”

GEC Security Symposium - image 2

GEC Security Symposium: Live Chat and Speaking Session

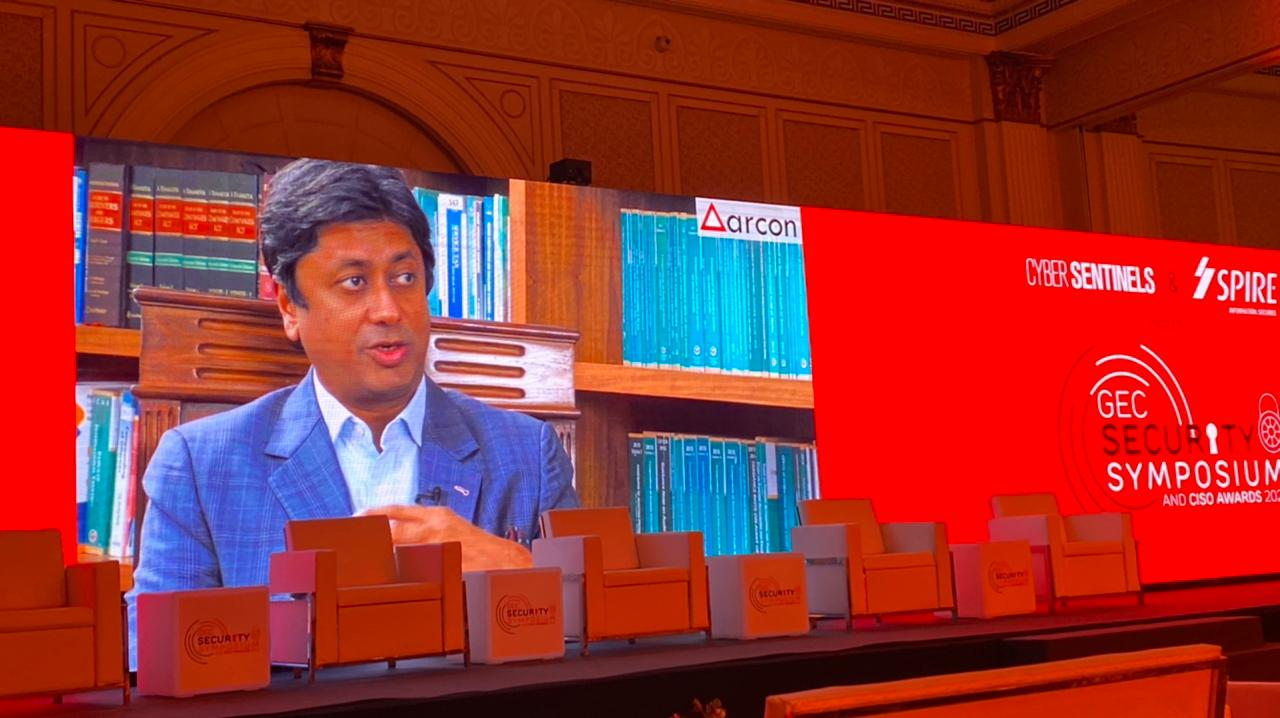
Cyber Sentinels also had an exclusive live chat and speaking session by ARCON’s Chief Mentor and Thought Leader, Mr.Anil Bhandari. With the topic of “Next gen Approach to Digital Identities and Vaults”, Mr. Bhandari shared his views on how Footprints of the (Digital) identities are moving out of the premise and converging into the cloud. While discussing his views on digital identities, here are some of the key extracts that attracted more attention from the chat session. 

  • What are Digital Identities?

As the world is embracing more digital technologies, every individual identity is converging into digital forms. These identities are digital identities that are likely to explode exponentially in every sphere of industries.

  • What are the threats associated with these digital identities?

There are multiple threats associated with digital identities. The footprints of identities are moving out from the homes and are converging themselves into the cloud. For large organizations, the entire technology structure is likely to reside in the cloud. Hence, the identities suddenly move from on-premise to cloud data centers. All kinds of identities are exploding including OS databases, human identities, and machine identities top the list. Once the digital footprints are compromised, the cyber criminals literally take away the digital lives of the victims because each and every activity would no longer remain secret.

  • Why are digital identities the core of cyber security?

Because it is omnipresent. The larger footprints of the identities, the ever-increasing number of identities, and the vulnerabilities of the identities – everything poses a huge risk. This is because we never come to know who is spying on or trying to compromise which identity at what point of time. For that reason, digital identities have to be the core of cyber security protection programs and very closely monitored.

  • Will that say “Digital World” is phenomenal and thus the digital identities are under risk?

Absolutely! As digital identities are entering every complex infrastructure, even in the cloud, these identities need to be protected. Otherwise, the privacy of an identity that we speak about, would be compromised. Hence, the privacy control mechanisms have to go to the next level. 

  • Do demographics really matter in managing privacy of digital identities? Especially for the UAE, what do you think about it?

Well, whether it is UAE, USA or any other country, the demographics do make a difference to the threat vectors that are coming in. For example, in developed countries like the USA, where lots of digital identities are floating around everywhere, there could be all kinds of cyber attackers coming after these identities. For countries like the UAE, there could be a large number of nation state actors coming after the individuals because of the local habits of the organizations regarding maintenance of privacy. In a country like Japan, as the community is closely guarded by the Government initiatives with even the smallest of security aspects, any incident, even if unexpected, fails to create a big impact. Hence, geographies and the geo-political arena definitely have an impact on controlling identity threats and understanding what kind of threats are coming around. 

  • Is the UAE the first point of hacking incidents?

Not really, but there are continuous and concentrated attempts to dismantle manufacturing, financial services, and other industries in that region. So the security mechanism adopted in that region should include monitoring and securing the privacy of digital identities.

  • What proactive measures should be taken to stay resilient to cyber threats?

Well anything and everything that is adopted should be less complex and more result-oriented. However, the most important thing should be to build up a resilient framework where responses are automated for any signal that is received. Technology like User Behaviour Analytics (UBA) helps to get into the logs of the identities quickly and in the right manner to analyze the risk factor. Today, it is no more important to invest in the best of the best technologies but the problem statement has to be clear and a relevant solution has to bring in.

  • That should include the identities too?

Well, not necessarily, but identities are the gateways to confidential business assets. Hence it should be on the priority list even if not as the top-most priority. For example, user authentication and user authorization are the mechanisms that could ensure that the right user is accessing the right system at the right time for the right purpose. Eventually, it ensures data security.

  • ARCON has already gone global? What is your learning from the UAE market?

In the UAE, as per my experience and learning, there has to be analysis on deeper security aspects as this country has invested a lot on modern IT technologies to enhance and enrich each business. It includes cyber security and cyber control tools which most of the SMEs take quite seriously. There is no doubt on the awareness, there is no doubt on staying more advanced. The question is just to align the IT security requirements as per demand and ensure business continuity at the same time through continuous re-designing and re-thinking.

  • On the ending note, one suggestion that you would like to give to the IT professionals today.

For the CISOs specially, I’d suggest all to stay focused on the automation as much as possible. Not only that, rigorous testing of that automation process is very very important. At the same time, we shouldn’t get blown away by excessive automation because we need to have false positives. It could result in unsuccessful projects or even hindrance in day-to-day operations. There has to be a robust security mechanism that would help them to detect the real problem statement and take immediate action to resolve it. Hence rigorous testing of the use cases is highly critical.

GEC Security Symposium - image 3

GEC Security Symposium, thank you; and ARCON will be back next year!!!

ARCON whole-heartedly thanks Global CIO Forum and GEC Media for organizing this prestigious Security Symposium and CISO Awards 2021 in Dubai. ARCON is really proud to be recognized as the Cyber Sentinels Security Awards 2021 winner for Privileged Access Management and thanks Global CIO Forum for recognizing the efforts of Team ARCON. 

With this award as another ‘feather in the crown’, ARCON, as a brand, would look to give a bigger business push in the Middle East region, a region where ARCON is an undisputed leader. 

ARCON would like to thank all the other participants, visitors and the organizing team as well for making this award function a successful event!